Naar de inhoud
Niagara Indie Apps
Reverse Engineer Apps

Reverse Engineer Apps

See inside any program: hashes, strings, headers and entropy

Windows macOS Linux

Reverse Engineer Apps downloaden – gratis

De app is gratis te downloaden en te installeren. Hieronder zie je wat de eenmalige ontgrendeling omvat.

Binnenkort beschikbaar: de downloads verschijnen hier zodra de app uitkomt.

Reverse Engineer Apps ontgrendelen

Reverse Engineer Apps is free to try for 3 days on Windows, Linux and macOS. This one-time purchase unlocks it permanently with a license key, activated in the app on up to 2 of your devices.

$4.25 CAD eenmalig, maximaal 2 apparaten

Na aankoop ontvang je een licentiesleutel per e-mail. Voer die in de app in om hem op maximaal 2 van je apparaten te activeren.
Uitgelichte afbeelding van Reverse Engineer Apps

Overzicht

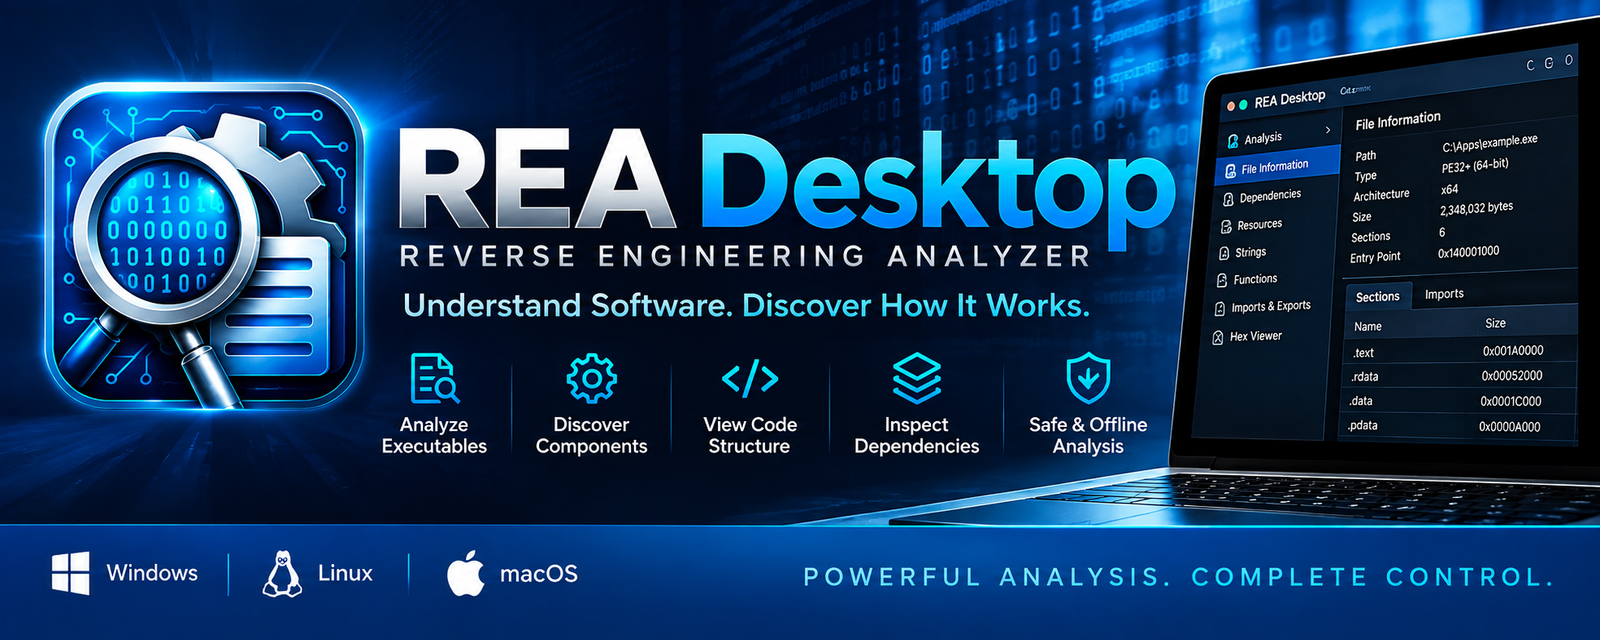
Reverse Engineer Apps is a desktop application for examining executables, libraries and other binary files without running them. It gives developers, security researchers, IT staff and students a clear graphical way to see what a file is made of. Pick a file and the app identifies its format, shows its metadata, calculates its SHA-256 hash, displays the hexadecimal header, extracts readable ASCII strings with their offsets, and measures byte entropy to help spot packed or encrypted data. Results can be exported as a JSON report. Your files stay on your computer. Local inspection works offline, and the app never executes a file just to inspect it. Nothing you inspect is uploaded unless you explicitly choose to send it somewhere. Deeper analysis features, such as running the full REA engine, project history and optional AI-assisted analysis, are still being developed and are not part of this description until they are finished and tested. Try the full app free for 3 days. After that, a one-time payment unlocks it for good on up to 2 of your devices. Open Source Acknowledgement Reverse Engineer Apps is developed and distributed by G Thompson / Niagara Indie Apps. It incorporates software from REA (Reverse Engineer Anything), an open-source project developed by morluto and its contributors. Original repository: https://github.com/morluto/rea The original REA software is licensed under the MIT License. Copyright (c) 2026 morluto. The original REA developers retain their respective rights to their contributions. Niagara Indie Apps independently develops and maintains the desktop application and its original components. Niagara Indie Apps is not affiliated with or endorsed by the original REA project. The complete original licence and the notices for other components are inside the app, in the About section under Open source credits.

Functies

File format identification

See what kind of file you have, even when the name says otherwise.

Metadata inspection

Read a file's size, type and other details at a glance.

SHA-256 hashing

Get a file's fingerprint to verify it or compare it with another.

Hex header view

Look at the raw bytes at the start of any file.

Strings extraction

Pull out readable text with the offset where each string was found.

Entropy analysis

Measure how random a file's bytes are, to help spot packed or encrypted data.

JSON report export

Save your results as a report you can keep or share.

Local and private

Works offline. Files are never run or uploaded without your say-so.

Wat het doet

A desktop tool for inspecting files and software. Identify file formats, read metadata, compute SHA-256 hashes, view hex headers, extract strings and measure entropy. Runs locally on Windows, Linux and macOS.

Systeemvereisten

A 64-bit desktop computer running Windows, Linux or macOS. No internet connection is needed to inspect files; a connection is needed once to activate a license.

Privacy

Lees de privacy-informatie van deze app →

Support

For questions about Reverse Engineer Apps, use the Contact page and select this app, or email admin@niagaraindieapps.com. For license questions, include your Device ID from the app.

Hulp krijgen